Live at argus.buzz
See every attack.
Understand every incident.
Argus streams security logs through Kafka, detects attacks with 15 rules mapped to MITRE ATT&CK, and explains each incident in plain language.
15 detection rules · 12 ATT&CK techniques · runs with no API keys
Correlating alerts from this source…
How it works
- 01
Ingest
Simulated attacks and real probe traffic from the live server.
- 02
Stream
Kafka, keyed by source.
- 03
Normalize
Three log formats, one validated event.
- 04
Detect
15 rules: signatures, windows and baselines.
- 05
Correlate
One incident per source, with repeat alerts throttled.
- 06
Explain
GeoIP, AbuseIPDB reputation and a written summary.
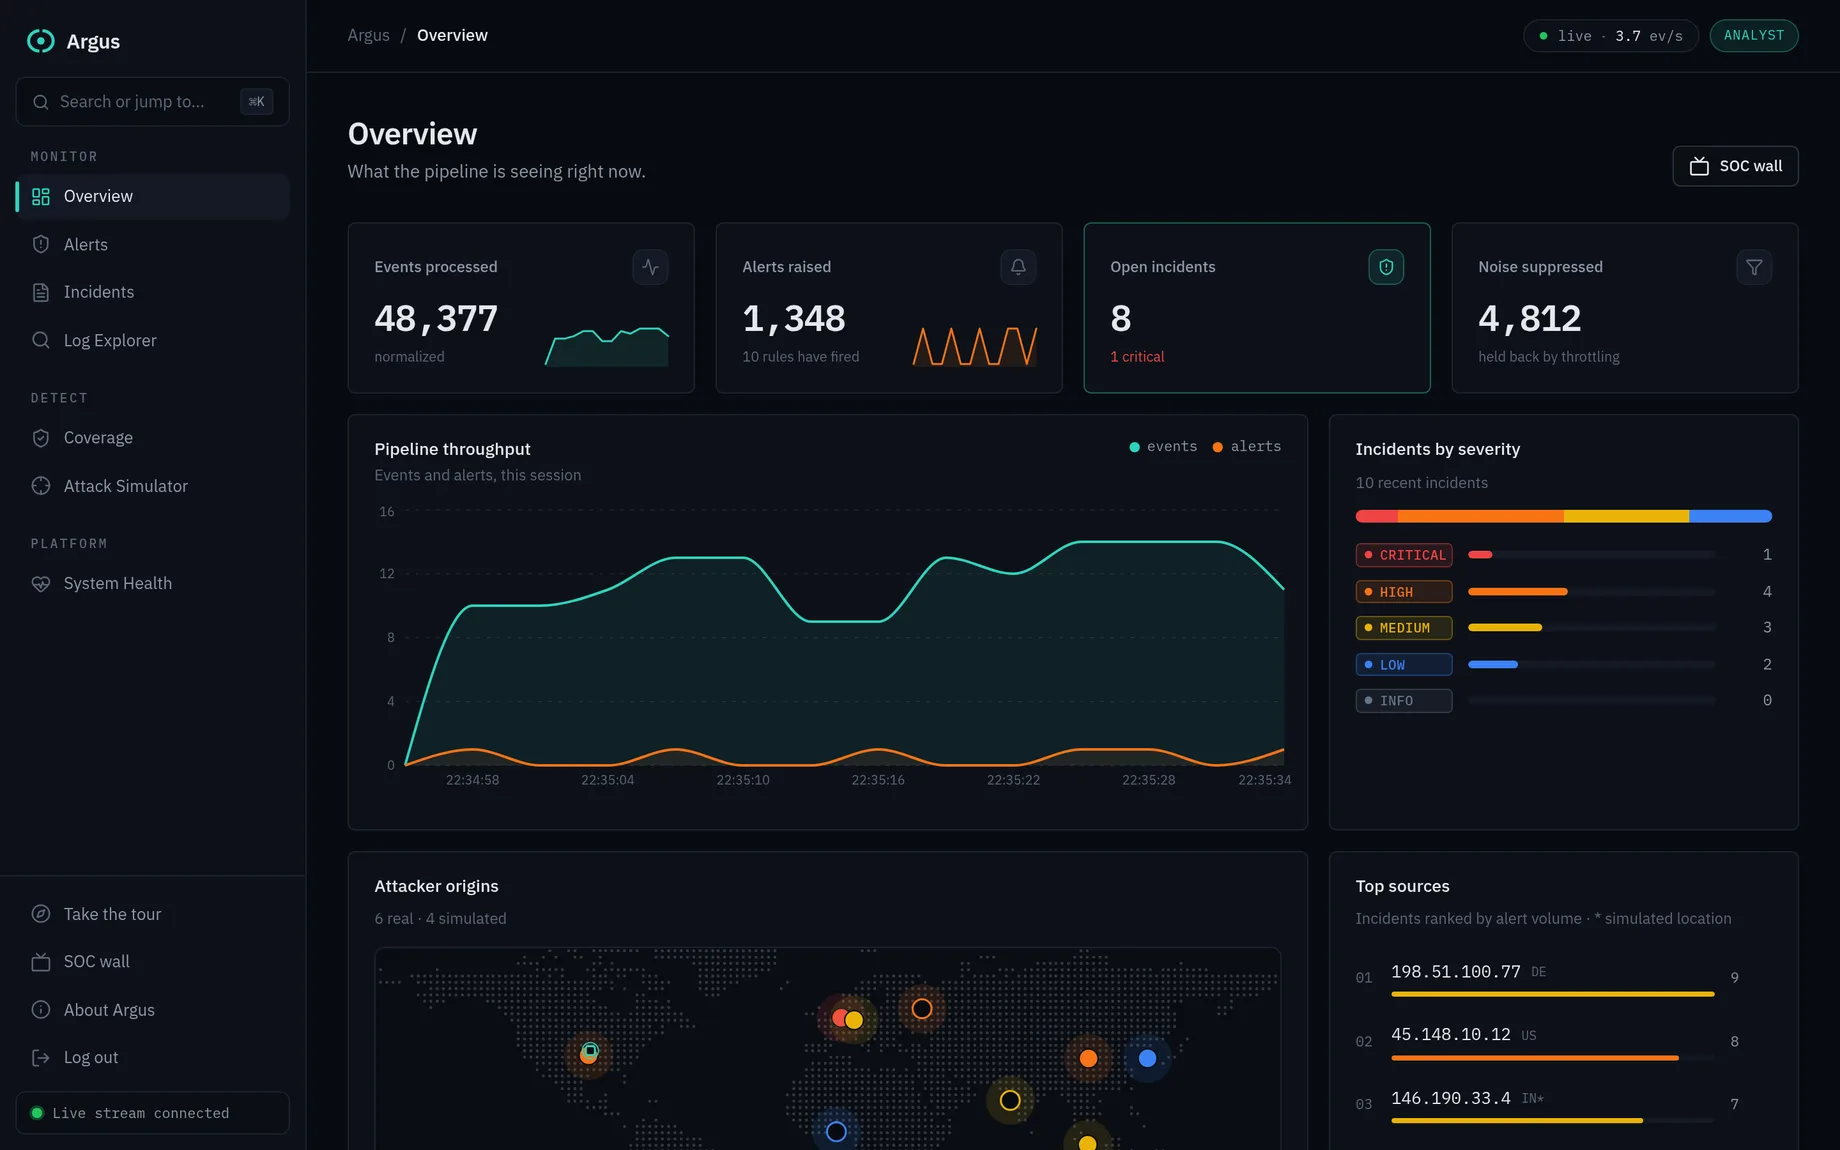
Inside the console
Throughput, severity and where attacks come from.
ATT&CK coverage
Every rule maps to a MITRE ATT&CK technique.
15 rules, 12 techniques, 6 of the 14 enterprise tactics.
What it does
Real attack traffic
Scanners probing the live server become real incidents.
Seven failed logins for deploy, then a success from the same address. Treat the account as compromised.
Written summaries
Each incident gets a short account of what happened and what to do next.
GeoIP and threat intel
Every public source is located and checked against AbuseIPDB.
Alert throttling
A scanner sending thousands of requests stays one readable incident.
Attack simulator
Ten scenarios you can fire at the live pipeline.
Security
- 01Supply chain
- CodeQL, gitleaks and Trivy on every push.
- 02Transport
- TLS, strict CSP and HSTS.
- 03Abuse
- Rate limits on the real client IP.
- 04Access
- Admin, analyst and read-only roles. No public sign-up.
- 05Runtime
- Scanned images, non-root containers.
Watch it catch an attack.
Sign in with the read-only demo and fire a scenario.
- 22:04:01firedaccount-takeover
- 22:04:01parsed8 auth events
- 22:04:02alertSSH brute force · T1110.001
- 22:04:02alertLogin after brute force · T1078
- 22:04:02incidentopened for 185.224.128.17
- 22:04:05summarywritten